
Hello!
Sitting at my desk, watching the field outside slowly turn from green to gold to dust, I am often reminded of growing up in drought-stricken California – finally, courtesy of climate change, the Netherlands feels like home.
While here in South Holland the dykes haven’t collapsed yet and we’re still a ways away from the drinking taps running dry (the irrigation taps, however, are being turned off), some people in Minnesota recently got a taste of the latter for a rather different reason: a suspected Iranian cyberattack on dozens of water and wastewater facilities, a campaign which quickly expanded to 11 other states.
At Binding Hook, we’ve been warning about cyber threats to critical infrastructure for a while, but seeing those threats play out is more concerning than vindicating.
Read Gijs van Loon, Apolline Rolland, James Shires, and Max Smeets’ 2025 article on what Europe can do to protect its water and wastewater infrastructure from similar threats.
Ironically, the elements targeted were programmable logic controllers (PLCS) – the same type of components that US-Israeli Stuxnet used to target the Iranian nuclear program. They’re also the same ones used by Iran-linked attackers in 2023 to target… US water and wastewater facilities. Maybe we should have seen this one coming (though you can hardly blame all of the people who no longer work at CISA for not doing the jobs they no longer have with the funding that no longer exists).
Besides, Iran is widely known for retaliatory cyberattacks – the weirder part of this one, as pointed out by Tom Uren, is how long it took. Especially given that CISA released an advisory in April warning about exactly this type of activity, several months before we saw any results.
In the 2023 case, the CyberAv3ngers hacktivist group, associated with Iran’s Islamic Revolutionary Guard Corps (IRGC) seemed to be targeting Unitronics PLCs specifically because they were made in Israel, a claim that has not yet been made about the American Rockwell PLCs targeted in the latest series of attacks. Despite that difference, some analysts think CyberAv3ngers is behind the latest series too, though recent warnings and claims from Iranian Ministry of Intelligence linked-Handala to have hacked other systems, uh, muddy the waters.
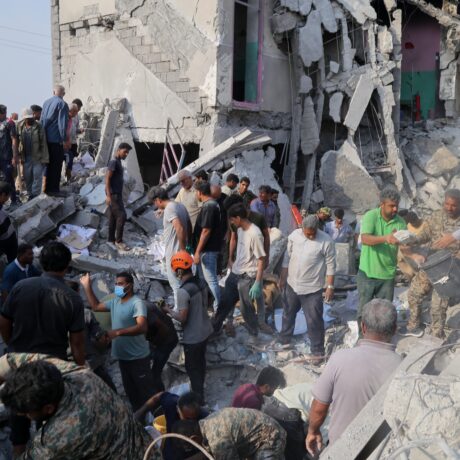
While the actual consequences for Minnesotans so far were just mild inconvenience – water plants down for a couple hours, low pressure in pipes, very temporary advisories to conserve and boil water – it will have been the first physical impact of the war for many, the first sign that the war could directly affect Americans beyond rising prices. And the rush of cyberattacks, sources and consequences not always known, just keeps coming: dams already a decade ago, medical devices and fuel tanks yesterday, ports tomorrow.
At the same time, it is one of those things that reminds you of the imbalance between ‘cyber war’ and good old missiles and drones. The impact of this ‘unprecedented wave of disruptive cyberattacks’ has nothing on the rather less temporary destruction of water tanks in southern Iran by US bombs and the alleged strikes on desalination plants in Iran by the US and, in turn, in Bahrain by Iran (the destruction of civilian water infrastructure is, by the way, a war crime).
President Donald Trump was quick to blame the ‘grossly incompetent’ and ‘corrupt’ state and governor of Minnesota for the initial outages there, rather than Iran. Given the expansion of known targets to Trump-friendly states like South Dakota and Georgia, I’m expecting a CISA advisory warning about threats from APT651 (aka Purple Rain or Nice Loon) any day now.
Until next month,
Katharine Khamhaengwong
Binding Hook Senior Editor
More Binding Hook on Iran:
- Gil Baram and Noya Peer review the cyber aspects of the 2025 war between Iran and Israel.
- Aleksandar Milenkoski, Jiro Minier, Julian-Ferdinand Vögele, Max Smeets, and Taylor Grossman take a closer look at the ways Iran uses ransomware.
- James Shires, Max Smeets, and Hannah-Sophie Weber examine Predatory Sparrow, an alleged hacktivist group targeting Iran.
Related Posts

Whose job is it to defend a private company?
25 August 2026
Hooked! #10: A month of Iran leaks and leakers
18 December 2025